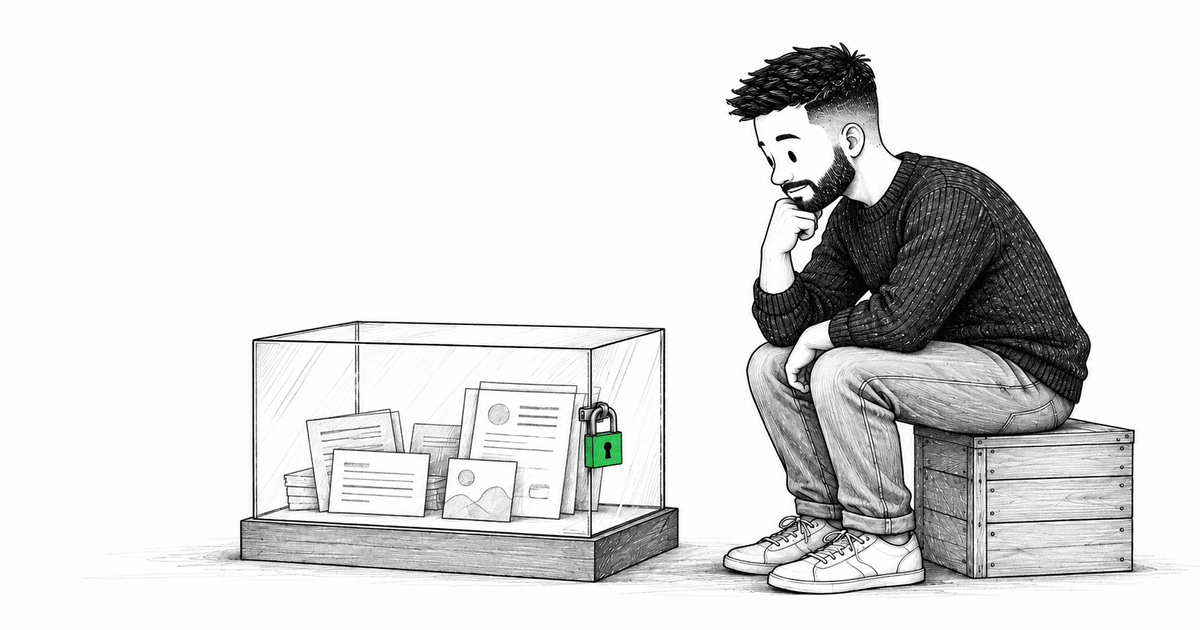
Read-Only Is Not the Same as Safe
Preventing writes protects one boundary. An agent may still read sensitive data, send context to services or expose it in outputs. I want those paths explicit.
7 min read
Preventing writes protects one boundary. An agent may still read sensitive data, send context to services or expose it in outputs. I want those paths explicit.
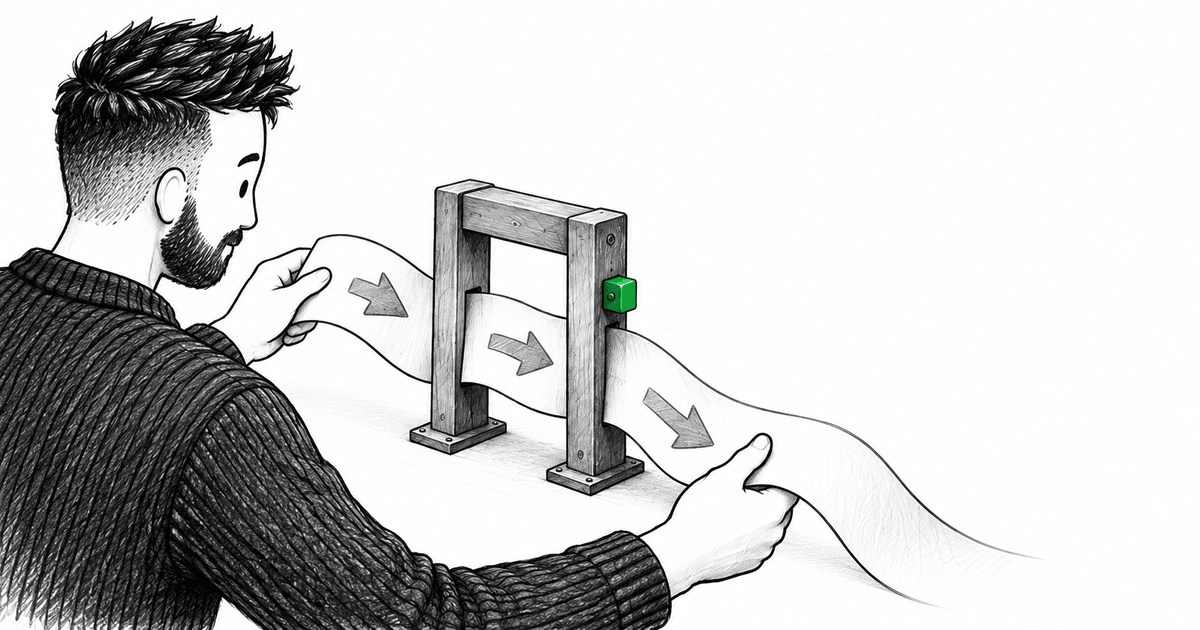
A coding agent must read repository content without treating it all as authority. I want the boundary between useful evidence and instructions to stay visible.

Taking a payment looks like a form submission and is nothing like one. The card number is radioactive, the confirmation is asynchronous, and the one thing your React app must never do is believe it got paid because a callback said so. Here's where the real line sits between the browser, your server, and Stripe.
Auth looks like a login form and turns out to be an architecture decision. Where do tokens live, who guards a route, what happens when the session dies mid-request? Here's why I buy auth instead of building it, and the parts that stay yours no matter what you buy.